GRC · AI Governance · Cybersecurity

Compliance that's bolted in, not bolted on.

I'm Shazia Saeed. For 15+ years at PwC, ReliaQuest, Protiviti and Accenture, I've built governance, risk and security programs from nothing and gotten them adopted across global organizations. Then I automate them, because a developer is still who I am at heart.

CISACDPSEITILCCSP · in progress
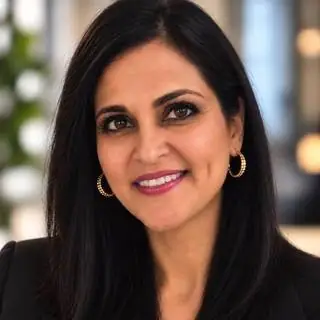
Portrait of Shazia Saeed
151Member firms in the global compliance program I built for PwC
55%Reduction in security risk in year one
83–90%Less manual compliance effort with agentic AI
$625KMeasurable cost savings from automation
$450MProduct revenue under my GRC program
15+Years in GRC, cyber, audit and risk
Who I work with

For leaders who need governance that people actually follow.

Boards & executives

Turn compliance into a business case

I advise CIOs, CISOs, legal counsel and boards on GRC strategy in terms of revenue, contracts and insurance, which is the language leadership acts on.

  • Enterprise GRC program design
  • Board & audit committee reporting
  • Quantitative risk (FAIR)
Security & engineering teams

Make compliance invisible to the work

I speak engineering's language. Controls get embedded in the pipeline, evidence gets collected automatically, and audits stop being a fire drill.

  • Agentic AI compliance automation
  • AI controls & NIST AI RMF
  • BCDR & operational resilience
Emerging leaders

Grow the next generation of security leaders

I've trained people with no security background into senior roles, and I lead mentorship for high-achieving women in security.

  • 1:1 mentoring
  • Team capability building
  • Women in security circles
My story

A developer who moved into risk.

Accenture hired me straight out of college and told me I'd be a database administrator for a telecom company. It was sink or swim. I built a network of DBAs around me and learned on the job, then went on to deliver ERP systems and custom applications for large enterprises.

When I moved into risk management at PwC, I kept that engineer's lens. My first compliance role uncovered a 49% ITGC deficiency rate. Within a year we had brought it down to 6%, and I was handpicked to build PwC's first global information security compliance program. Others had tried before and stalled. I built it from scratch and took it across 151 member firms.

Since then I've led risk and compliance at ReliaQuest, an AI cybersecurity company serving 1,300+ enterprise clients. I returned to PwC to run GRC and business continuity for a $450M product portfolio, where I built AI agents that do the manual work for us.

You can take the girl out of technology, but you can't take the technology out of the girl.
Selected work

Programs built from zero and adopted at scale.

Each one written up the way I'd document a finding: what was wrong, what I did, and what changed.

PwC Global · 2017–2022

PwC's first global security compliance program

55%reduction in security risk in year one, plus $2M in cost savings
Finding

151 independent member firms with no consistent information security compliance. Earlier attempts had stalled because of the complexity.

Action

Before rollout I met every CISO individually and framed compliance as a way to win more clients. I placed regional team members across the Americas, EMEA and APAC and built a unified controls framework where one piece of evidence satisfies many controls. I reviewed automated dashboards weekly with the Global Chief Risk Officer.

Outcome

Delivered on time and within budget. The program ran as a centrally ISO-certified shared service, and its revenue funded ongoing cybersecurity investment across the network. No CISO wanted to be the red dot on the CRO's dashboard.

PwC Products & Technology · 2023–2026

GRC for 30+ products with no executive mandate

Board-mandatedafter starting as an informal, grassroots practice
Finding

Commercial digital products earning $450M a year had no shared GRC framework and no executive sponsor for one.

Action

I led with business impact instead of compliance language. I showed product leaders where missing controls conflicted with customer contracts they had already signed, which made compliance a customer-retention issue. Legal, Risk & Quality and Contracts became advocates.

Outcome

A framework anchored in NIST CSF, NIST AI RMF, COBIT, ISO 27001 and SSAE 18. We closed 10 high-risk findings and rolled out repeatable remediation playbooks enterprise-wide.

ReliaQuest · 2022–2023

Four audits at once, with no audit fatigue

1×process owners contacted once instead of four times
Finding

An AI cybersecurity company serving 1,300+ enterprise clients needed SOC 2 Type 2, ISO 27001, PCI-DSS and HIPAA audits each year.

Action

I kicked off all four audits together on a common controls framework in LogicGate, so evidence collected once satisfied every framework. I also turned customer assurance into a sales enabler and built a four-tier vendor risk program.

Outcome

Shorter audit timelines and far less burden on process owners. Third-party risk went from ad hoc requests to a consistent process.

PwC Finance · 2012–2017

Restoring confidence in financial controls

49% → 6%ITGC deficiency rate, within one year
Finding

Critical gaps in IT general controls put the reliability of financial statements at risk.

Action

I led SOX/ICFR scoping, tracked remediation rigorously with steering committee escalation, and redesigned SAP Financials security to remove segregation-of-duties conflicts.

Outcome

Senior leadership noticed the turnaround, and it led directly to the global security compliance mandate.

Agentic AI in practice

Three AI agents that do the manual work.

Automation only works on a sound process, so I prove the manual version first. These are the three I built at PwC.

Privileged access review

Access reviews with no human dependency

Pulls elevated accounts from Azure, VMs, databases, ADO and GitHub and matches them against team rosters. Only exceptions go to approvers. Accounts marked invalid automatically open a ServiceNow ticket for termination.

6 weeksmanual
→
4 hoursautomated
Critical asset inventory

Configuration drift caught as it happens

Scans every resource in the Azure subscription, rates its criticality and baselines its configuration. It has flagged a production database with encryption turned off, storage made public, and logs that stopped reaching the SIEM.

Auditfound later
→
Hoursflagged live
BCDR validation

DR architecture checked against business need

A custom GPT compares the DR architecture with recovery time and recovery point requirements from the business impact analysis. It recommends the right DR pattern and generates a remediation plan when they don't match. Tested across 30 products.

Manualper product
→
30products
83–90%less manual compliance effort$625Kmeasurable cost savings
How I think

Confidence in compliance should come from how the program runs, not from a scramble before each audit.

Tone at the top

When leaders are bought in, half the battle is won. Their mandate drives adoption and accountability.

Control ownership

Controls don't run themselves. Every control needs a named owner who is held to it.

Evidence integrity

Harvest evidence straight from source systems. That removes human error, omissions and inconsistency.

Strong issue management

Every finding gets an owner, a plan and a due date, with automatic escalation when SLAs slip.

Continuous monitoring

A live signal that controls work every day, not a quarterly snapshot.

AI governance

Most AI controls are ones your team already knows.

When I built PwC's AI controls framework on the NIST AI RMF, 80% of the controls turned out to be conventional IT general controls. Only 20% were truly AI-specific, and that's where teams should spend their attention.

Already familiar

  • Access management
  • Change management
  • Incident response
  • Resilience

AI-specific

  • Hallucination
  • Bias & fairness
  • Data leakage
  • Model drift
  • Explainability
"Automations need sound processes." "Collect once, use many." "A defensible range beats an indefensible color." "Listen first, assess second, build third."
In their words

What colleagues say.

You have built rapport and trust with the Risk & Compliance team as well as teams across the business, and have brought structure and maturity to how the team operates. You have a high level of accountability and can be trusted to execute and get things done.
Chief Information OfficerReliaQuest, annual performance review
Her genuine interest in the other members and passion for cultivating a safe environment has rapidly increased our level of comfort in opening up to share our ideas, endeavors, and efforts.
Mentee, Women Security Leadership ForumShared with PwC senior leadership at an internal summit
Career

Two decades in technology, risk and assurance.

2023 – 2026

Director, Enterprise GRC, Compliance & Business Continuity

PwC

GRC, compliance engineering and resilience for 30+ commercial products ($450M), reporting to the Board of Partners. Built the AI controls framework and the agentic AI automations.

2022 – 2023

Global Head of Risk and Compliance

ReliaQuest

Enterprise GRC for an AI cybersecurity company with six global operating centers. Ran multi-framework audits, third-party risk, security awareness for 1,200 people, and the risk and compliance integration after the Digital Shadows acquisition.

2017 – 2022

Global Information Security Compliance Leader

PwC

Built the program across 151 member firms in a $57B network. Led a 14-person global team on a $2.3M budget.

2012 – 2017

Senior Manager, Finance Controls & Compliance

PwC

Led the ICFR and SAP Security teams. Owned SOX scoping and testing, reporting to the CFO, Controller and Audit Committee.

2008 – 2012

Independent Consultant & Advisor

Self-employed

ITGC, PCI-DSS and vendor governance across PeopleSoft, SAP, Oracle and SQL Server.

2005 – 2008

IT Risk Manager

Protiviti

SOX internal audits, data center security assessments, pre-implementation reviews.

Earlier

Senior Consultant · Solution Architect

Accenture · Visalign

ERP and custom application delivery across telecom, education and transportation. Started as a DBA.

Speaking

Bring this perspective to your stage.

I speak at corporate events about where compliance is heading, and how organizations can build the governance they'll need to stay ahead of AI.

Inquire about a talk

Governing AI without slowing it down

The 80/20 of AI controls, and why waiting for standards is the wrong move.

Global GRC adoption across 151 countries

What it takes to get independent firms to say yes.

Agentic AI for compliance teams

Turning six weeks of manual work into four hours, and what to automate first.

Leading change without authority

Clarity, visibility and consequences in place of a mandate.

Leadership & mentoring

Every person has different fingerprints.

I assess where each person is today, build a plan around their strengths, and use real work as the classroom. I've trained people with no security background who went on to senior roles. One is now a partner at KPMG.

At PwC I led a mentorship circle for high-achieving women in security through the Women Security Leadership Forum. Strong mentors invested in me, and I'm passionate about paying it forward.

Accountable

When I take something on, it gets done. That's the standard I hold myself and my team to.

Resourceful

When resources are tight, I find a way forward, whether that's sequencing scarce engineering time or putting AI to work.

Empowering

I invest in the people around me and have developed senior managers across three regions.

Daily brief

AI agent adoption, one short note a day.

Each morning I read what's new in how organizations adopt AI agents and write up one finding, with the sources so you can check it.

Loading the latest notes…

All notes →

Let's talk

Building something that needs to be governed well?

shasae099@gmail.com

Based in Tampa, Florida · Speaks English, French, Hindi, Urdu and Punjabi